
copied!
Key takeaways:
- Modern commerce stacks expand attack surfaces across APIs, cloud systems, third parties, payments, and customer identities.
- PCI DSS 4.0.1 compliance mandates strict client-side monitoring to prevent modern web-skimming and Magecart attacks.
- Strong ecommerce cyber security requires layered controls across architecture, identity, data, transactions, infrastructure, and integrations.
- Continuous testing, threat monitoring, AI-aware controls, and recovery planning help enterprises build resilient commerce platforms.
Modern commerce platforms are no longer a single application sitting behind a firewall. Headless storefronts, APIs, cloud services, payment providers, customer identity platforms, analytics scripts, mobile apps, and third-party integrations now work as one connected system. That architecture improves speed and flexibility, but it also creates more paths for attackers to exploit
The risk is measurable. Verizon’s 2025 Data Breach Investigations Report analyzed 22,052 security incidents and 12,195 confirmed breaches. In retail, 837 incidents were recorded, including 419 with confirmed data disclosure. System intrusion, social engineering, and basic web application attacks accounted for 93% of retail breaches
The implication is straightforward: ecommerce cyber security audit can no longer be limited to a perimeter or compliance exercise. Security has to be designed into the commerce architecture, transaction flows, software lifecycle, and operating model
Why The Modern Commerce Stack Creates A Larger Attack Surface
Modernizing a platform introduces the concept of distributed trust. A retailer can have strong internal controls around its core platform, while a connected API, inventory plugin, marketing script, external vendor, or federated identity service creates another route into the ecosystem. Every new integration point outside the direct corporate perimeter introduces potential risk, requiring security for ecommerce website operations to function dynamically across external dependencies.
How Attack Paths Move Through a Modern Commerce Stack
A security weakness rarely stays confined to one component. Attackers can move from identities, APIs, scripts, or vendors toward sensitive data and business-critical functions. Mapping these paths helps prioritize controls based on potential business impact
| Attack path | Exploited weakness | Business impact | Primary controls |
|---|---|---|---|
| Credential stuffing → ATO | Weak authentication | Unauthorized orders, loyalty theft | Adaptive MFA, bot management, risk scoring |
| Malicious script → payment-page compromise | Uncontrolled third-party JavaScript | Payment-data theft | CSP, script inventory, integrity monitoring |
| API abuse → business logic manipulation | Broken authorization | Price/order manipulation | Object-level authorization, schema validation, rate limits |
| Vendor compromise → commerce environment | Excessive third-party access | Data or operational compromise | Vendor isolation, least privilege, monitoring |
| Bot → card testing | Weak transaction controls | Payment fraud, processor fees | Bot detection, velocity rules, payment intelligence |
9 Top eCommerce Cybersecurity Risks
The most significant ecommerce security issues are not isolated website vulnerabilities. They emerge where customer identities, payments, APIs, business processes, and external services intersect. Effective risk management starts by understanding which attack path can compromise which business function
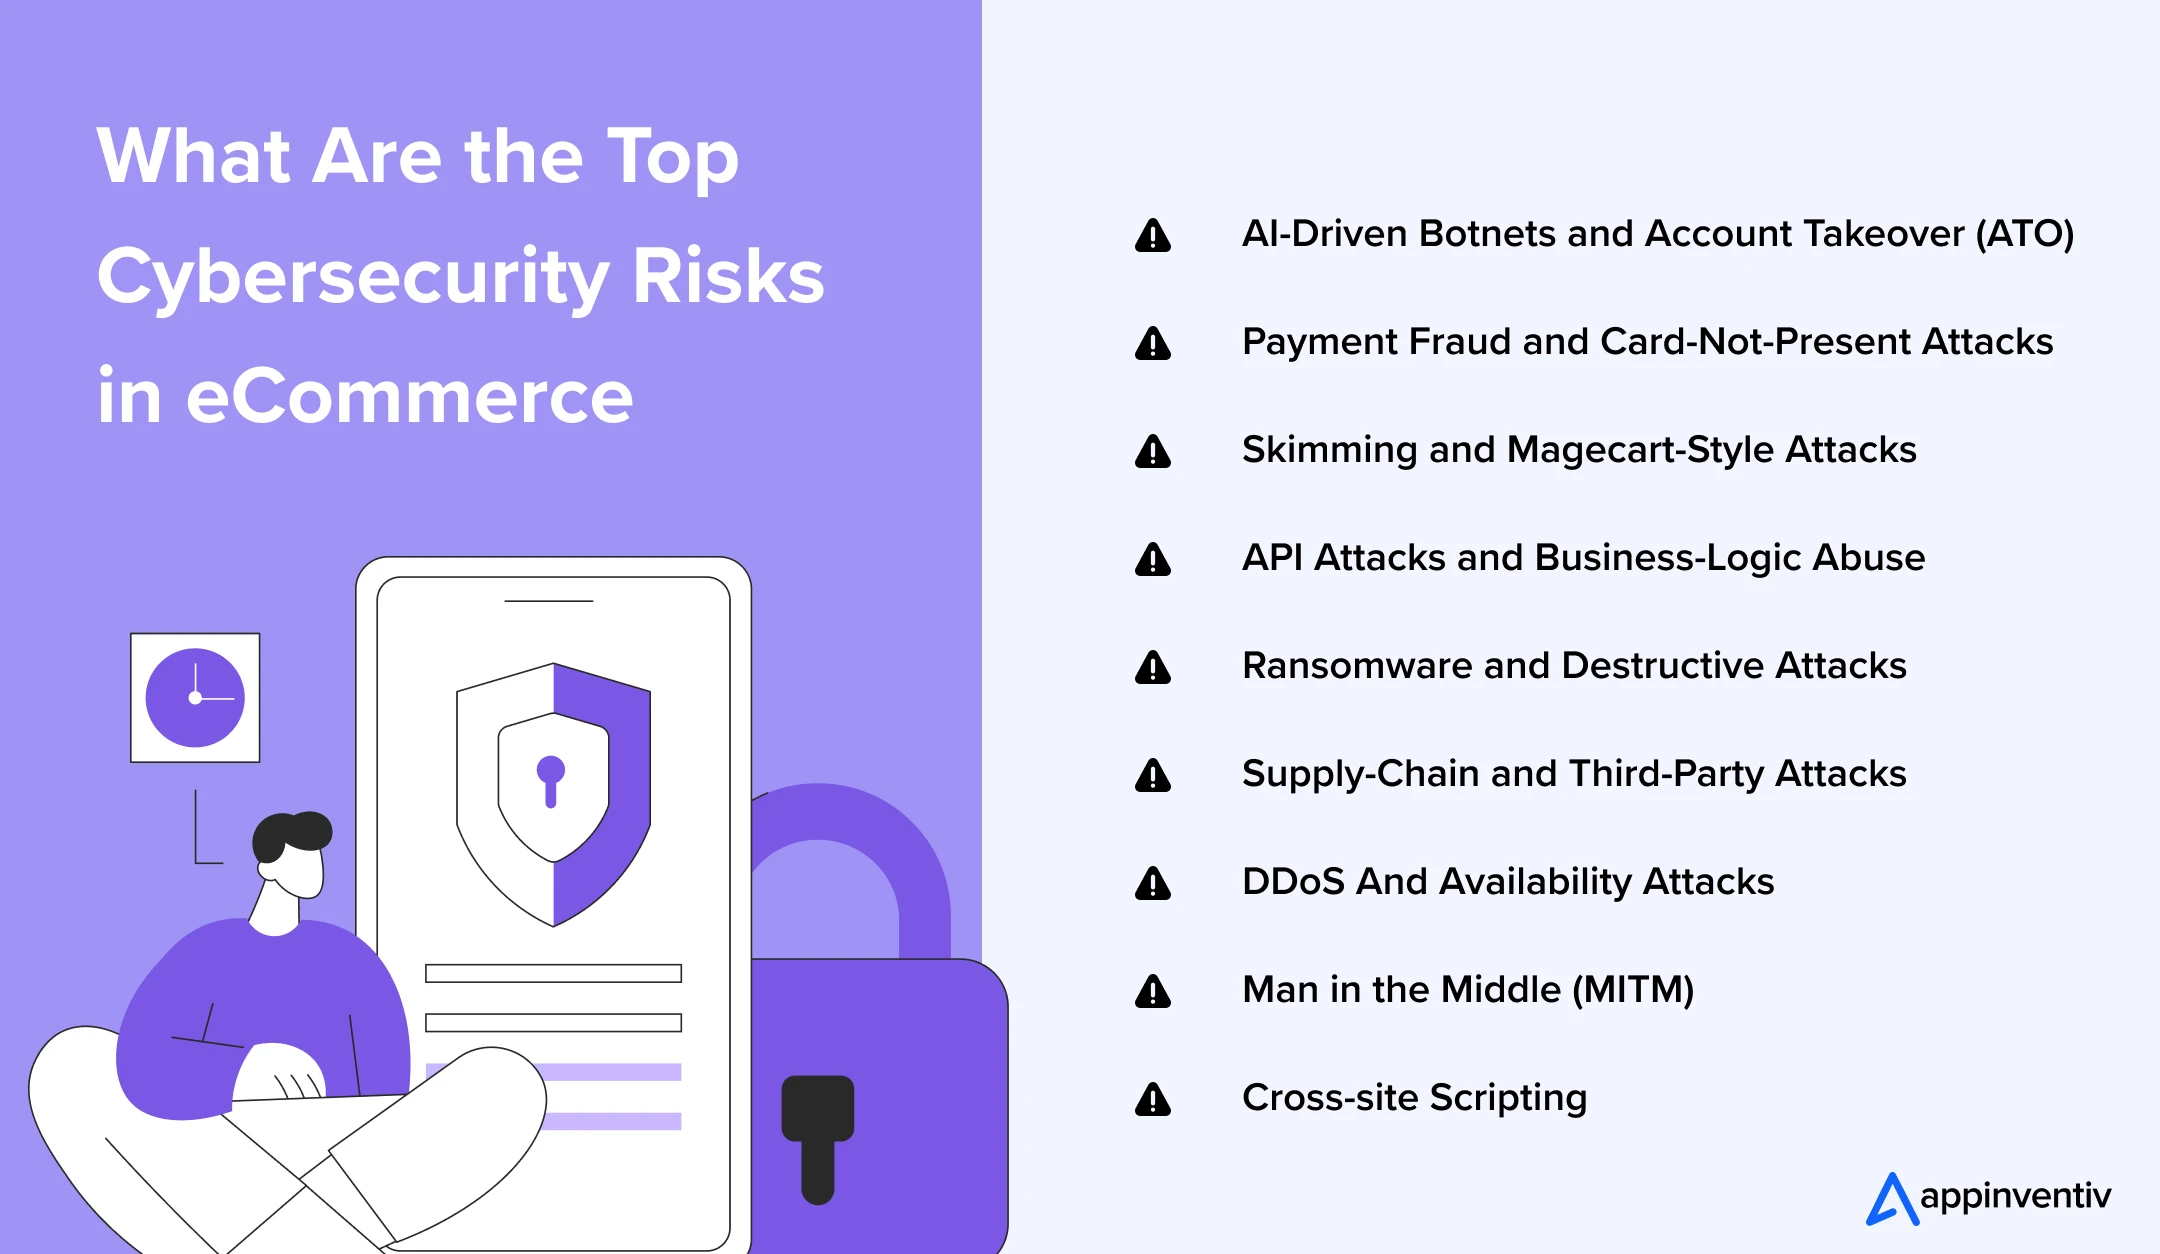
AI-Driven Botnets and Account Takeover
Automated botnets leverage stolen credentials to execute credential stuffing attacks at scale. These campaigns compromise user accounts to access stored payment methods, exhaust inventory logic, and extract loyalty points
Payment Fraud and Card-Not-Present Attacks
Card-not-present environments remain attractive because attackers can automate card testing, exploit compromised accounts, or manipulate checkout processes. Transaction controls must combine payment intelligence with identity and behavioral signals
E-Skimming and Magecart-Style Attacks
Malicious scripts can capture payment information directly from checkout pages. PCI SSC issued dedicated 2025 guidance addressing payment-page security and e-skimming controls under PCI DSS requirements 6.4.3 and 11.6.1
API Attacks and Business-Logic Abuse
Unsecured microservices expose core application logic to manipulation. Attackers exploit these endpoints to manipulate pricing algorithms, apply unauthorized discount codes, and extract sensitive database records without triggering alarms
Ransomware and Destructive Attacks
Malicious actors encrypt critical databases or operational environments, halting digital storefronts entirely. Enterprise recovery demands immutable backups and isolated staging areas to restore services swiftly without negotiating
Supply-Chain and Third-Party Attacks
Compromised external vendors or marketing integrations provide backdoor access into the primary commerce environment. Security teams must continuously monitor all integrated software dependencies for unauthorized logic modifications
DDoS and Availability Attacks
Distributed denial of service campaigns overwhelm application servers with artificial traffic spikes. These disruptions prevent legitimate shoppers from completing transactions and often serve as diversions for simultaneous data exfiltration
Man-in-the-Middle Attacks
Attackers intercept communication between the customer browser and the commerce server. By altering data in transit, adversaries steal session tokens, manipulate order details, or harvest unencrypted login credentials successfully
Cross-Site Scripting
Malicious scripts are injected into trusted web pages, executing within the browser of unsuspecting customers. This vulnerability allows attackers to hijack active user sessions, redirect shoppers, or bypass access controls entirely
What Does An Ecommerce Security Architecture Protect?
A secure commerce architecture protects more than the storefront. It covers customer identities, application logic, APIs, transactions, data, infrastructure, integrations, and the operational systems connecting them. Leaving any single layer exposed compromises the entire commerce operation
Customer Layer
Customer accounts, credentials, personal information, addresses, loyalty data, and identity attributes require strong authentication, authorization, session management, and privacy controls
Application Layer
The storefront, mobile applications, APIs, microservices, admin interfaces, and business logic must resist unauthorized requests, manipulation, injection, and application-layer attacks
Transaction Layer
Checkout, payment authorization, refunds, order modification, promotions, and gift cards require controls that protect both payment data and transaction integrity
Infrastructure and Ecosystem Layer
Cloud environments, databases, CI/CD pipelines,third-party services, POS systems, analytics tools, and connected devices extend the security boundary beyond the core platform
How to Design A Secure-By-Default Commerce Architecture to Protect Every Layer?
Security should be an architectural property rather than a collection of controls added after development. Each layer should have defined trust boundaries, least-privilege access, encryption, monitoring, automated testing, and recovery mechanisms. This reduces the likelihood that one compromised component can cascade across the commerce ecosystem
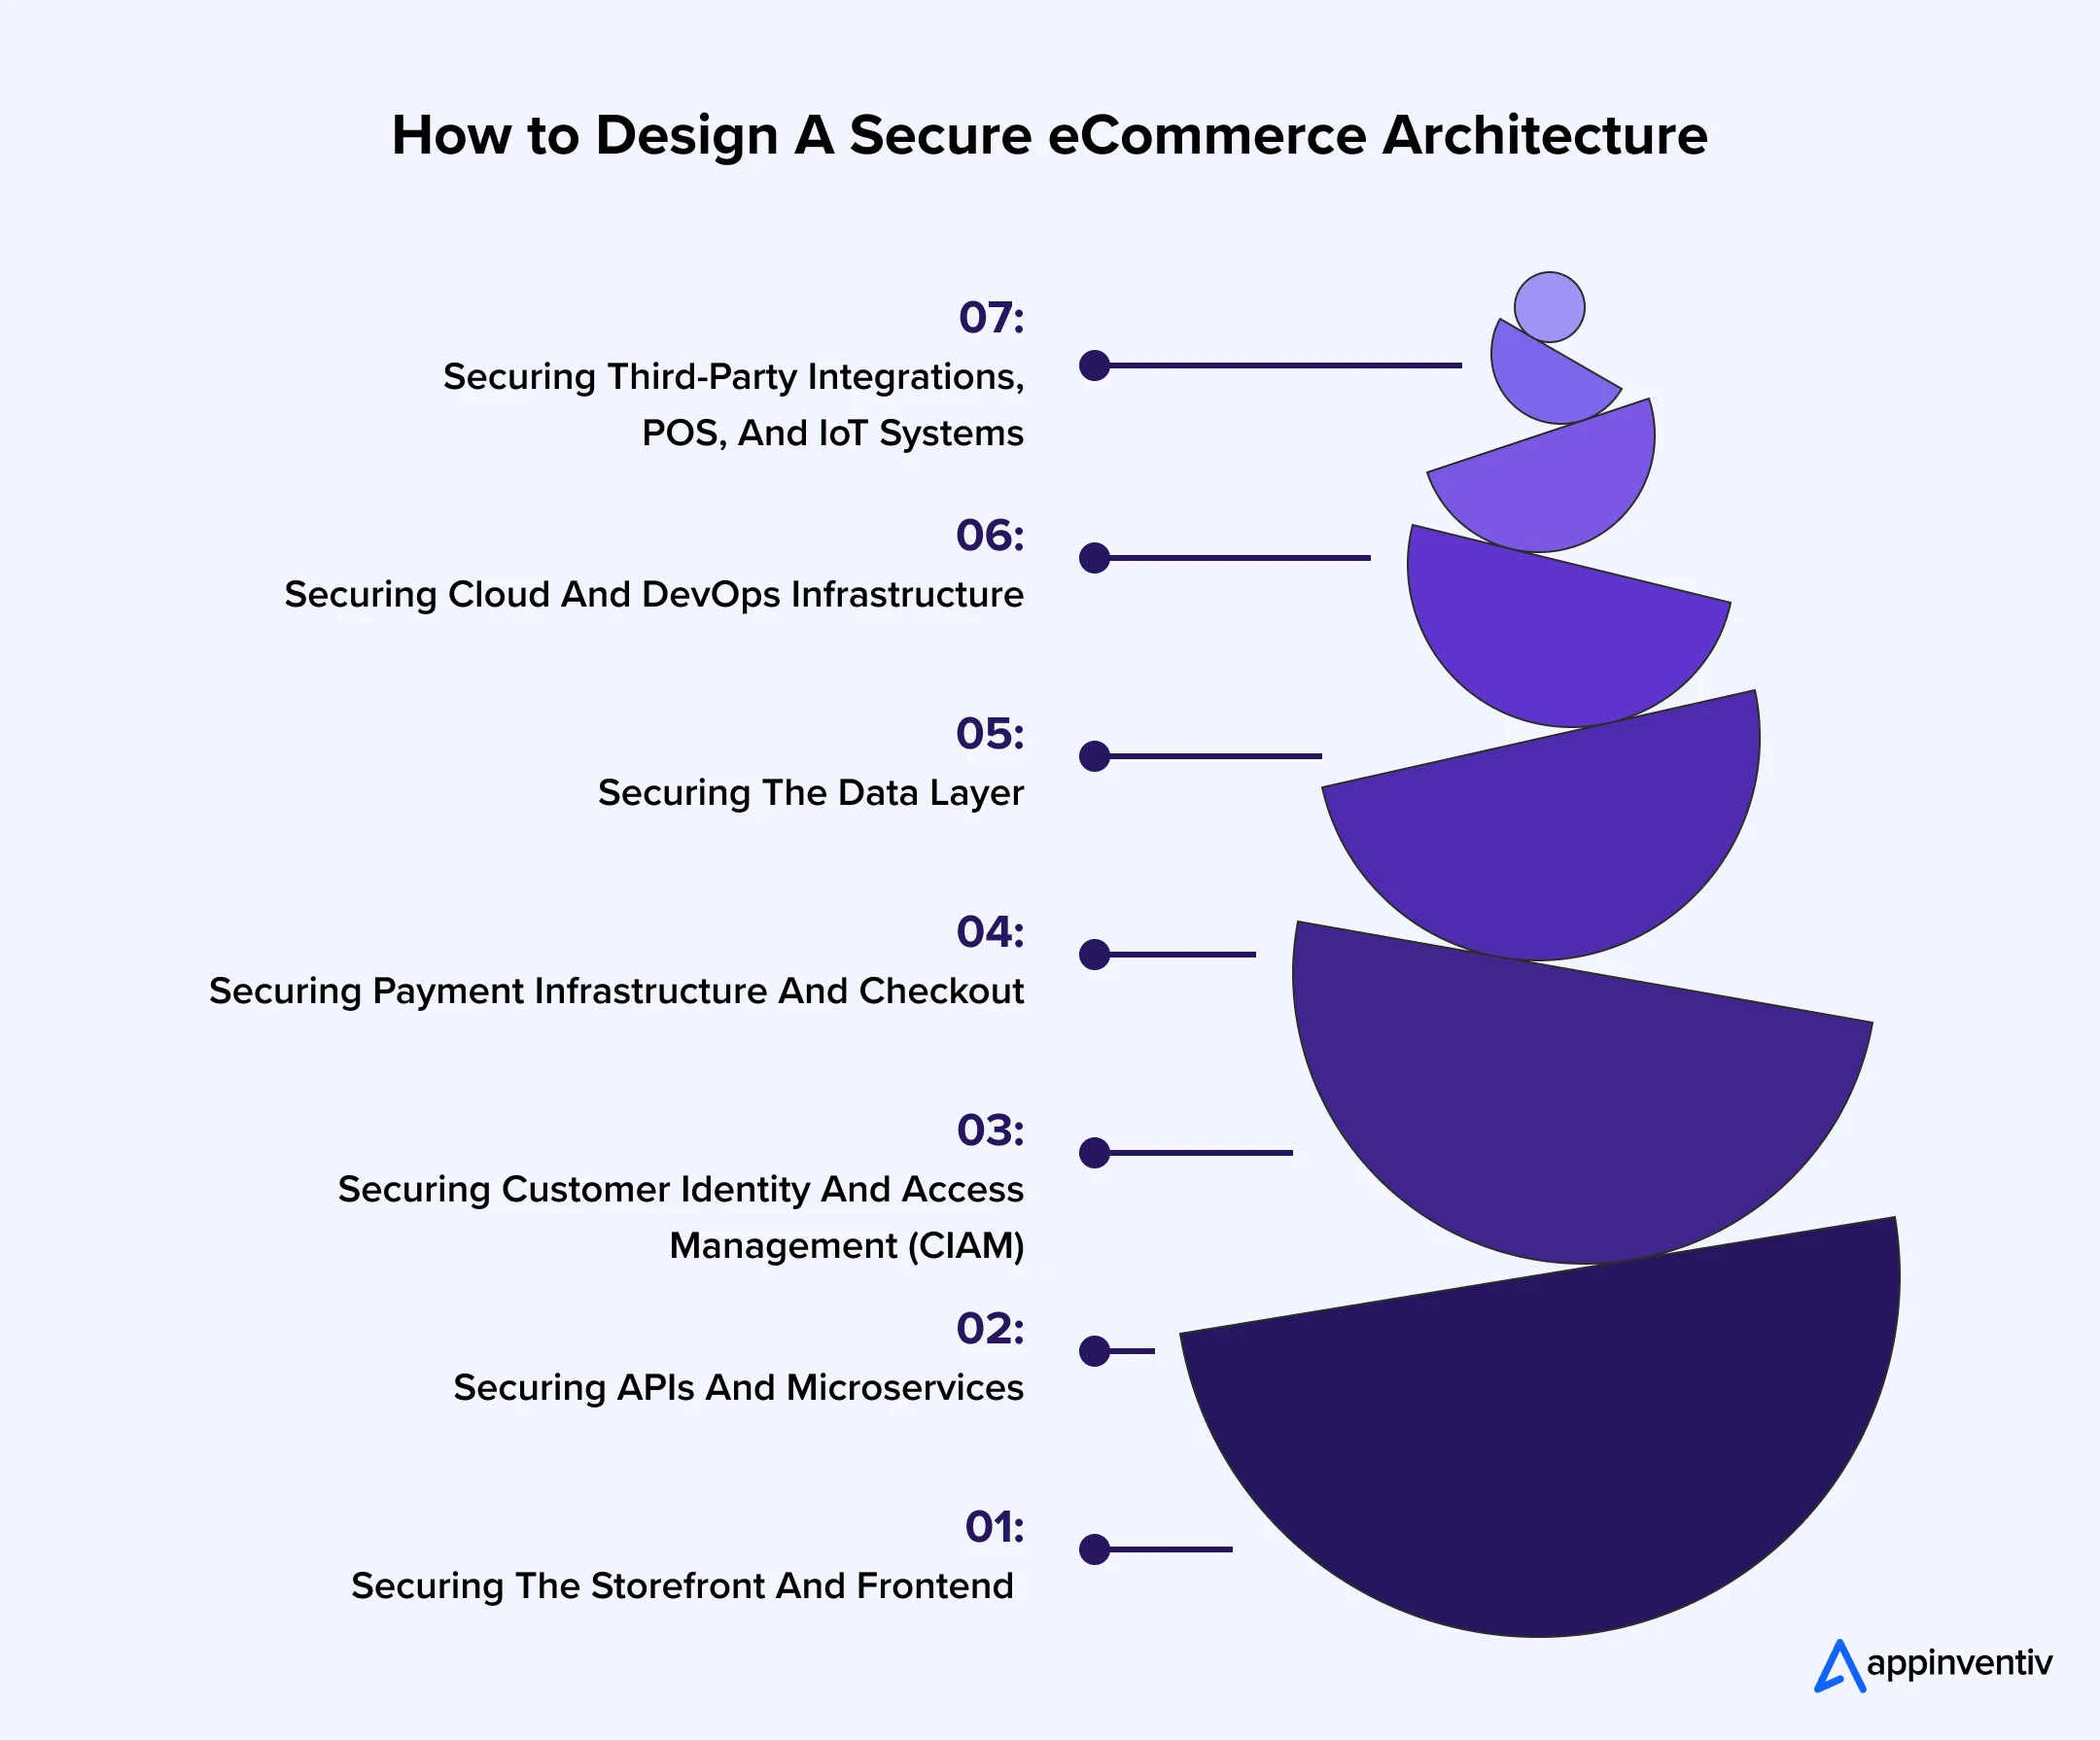
Securing the Storefront and Frontend
Use secure headers, CSP, dependency controls, input validation, protected sessions, and continuous client-side script monitoring. Keep third-party JavaScript to the minimum necessary
Securing APIs and Microservices
Apply strong authentication, granular authorization, schema validation, rate limiting, API gateways, secrets management, and service-level observability. Test business logic, not just endpoints
Securing Customer Identity and Access Management
Centralize CIAM controls around adaptive authentication, MFA, session security, account recovery, risk-based access, and least privilege. Treat customer identity as a security boundary
Securing Payment Infrastructure and Checkout
Minimize card-data exposure through appropriate payment architecture, tokenization, segmentation, secure payment integrations, and strict control over scripts operating on payment pages
Securing the Data Layer
Classify customer and business data by sensitivity. Encrypt sensitive information at rest and in transit, restrict database privileges, monitor unusual queries, and establish defined retention policies
Securing Cloud and DevOps Infrastructure
Security controls should follow infrastructure as code, CI/CD, containers, cloud identities, secrets, and deployment environments. Automated scanning should block material risks before production deployment
Securing Third-Party Integrations, POS, and IoT Systems
Inventory every dependency and establish ownership, access boundaries, security requirements, monitoring, and incident responsibilities. Connected devices should never receive broader network access than their function requires
What eCommerce Security Solutions Business Should Have in Place?
Deploying foundational security tools is non-negotiable for protecting retail platforms. These security controls help reduce a specific attack path without adding unnecessary operational complexity
| Security Control | Primary Purpose |
|---|---|
| HTTPS and TLS Certificates | Protect data exchanged between customers and commerce systems |
| Anti-malware and endpoint protection | Detect malicious activity across servers and endpoints |
| Secure server and admin panel | Restrict privileged access and harden management interfaces |
| Web application firewall | Filter malicious traffic and common application attacks |
| Secure payment gateway | Reduce exposure to payment-data compromise and transaction abuse |
Best Practices for Designing a Secure-by-Default Commerce Architecture
Implementing a secure architecture requires a strong commitment to continuous validation and strict governance. These best practices drastically reduce the risk of systemic compromise
Adopting a Zero Trust Architecture
Never trust any entity inside or outside the network by default. Verify every digital request explicitly before granting re
Navigating PCI DSS 4.0.1 Compliance
Implement continuous client-side monitoring to detect unauthorized script modifications. Ensure all payment page scripts are inventoried and strictly justified
Implementing Advanced Threat Intelligence
Utilize global threat data to anticipate emerging attack vectors proactively. Feed automated indicators of compromise directly into the security operations center
Build security into the SDLC
Integrate vulnerability scanning directly into the continuous integration pipeline natively. Catching architectural flaws during the coding phase drastically reduces remediation costs
Use multilayer security
Deploy overlapping defensive controls across networks, applications, and endpoints. If one mechanism fails, secondary systems contain the active threat securely
Use Firewalls
Configure next-generation web application firewalls to block anomalous traffic patterns. Filter malicious requests targeting specific microservices or vulnerable API endpoints
Secure your website with SSL certificate
Enforce TLS 1.3 across all internal and external communication channels. Guarantee that no plain text data traverses the public internet ecosystem
How AI Is Changing Cyber Security in eCommerce?
Artificial intelligence in cyber securityfor retail & eCommerce has fundamentally altered the landscape for businesses. Both defenders and adversaries utilize machine learning to scale their operations and identify vulnerabilities faster. Understanding this dynamic is critical for anticipating eCommerce security threats and deploying automated countermeasures effectively
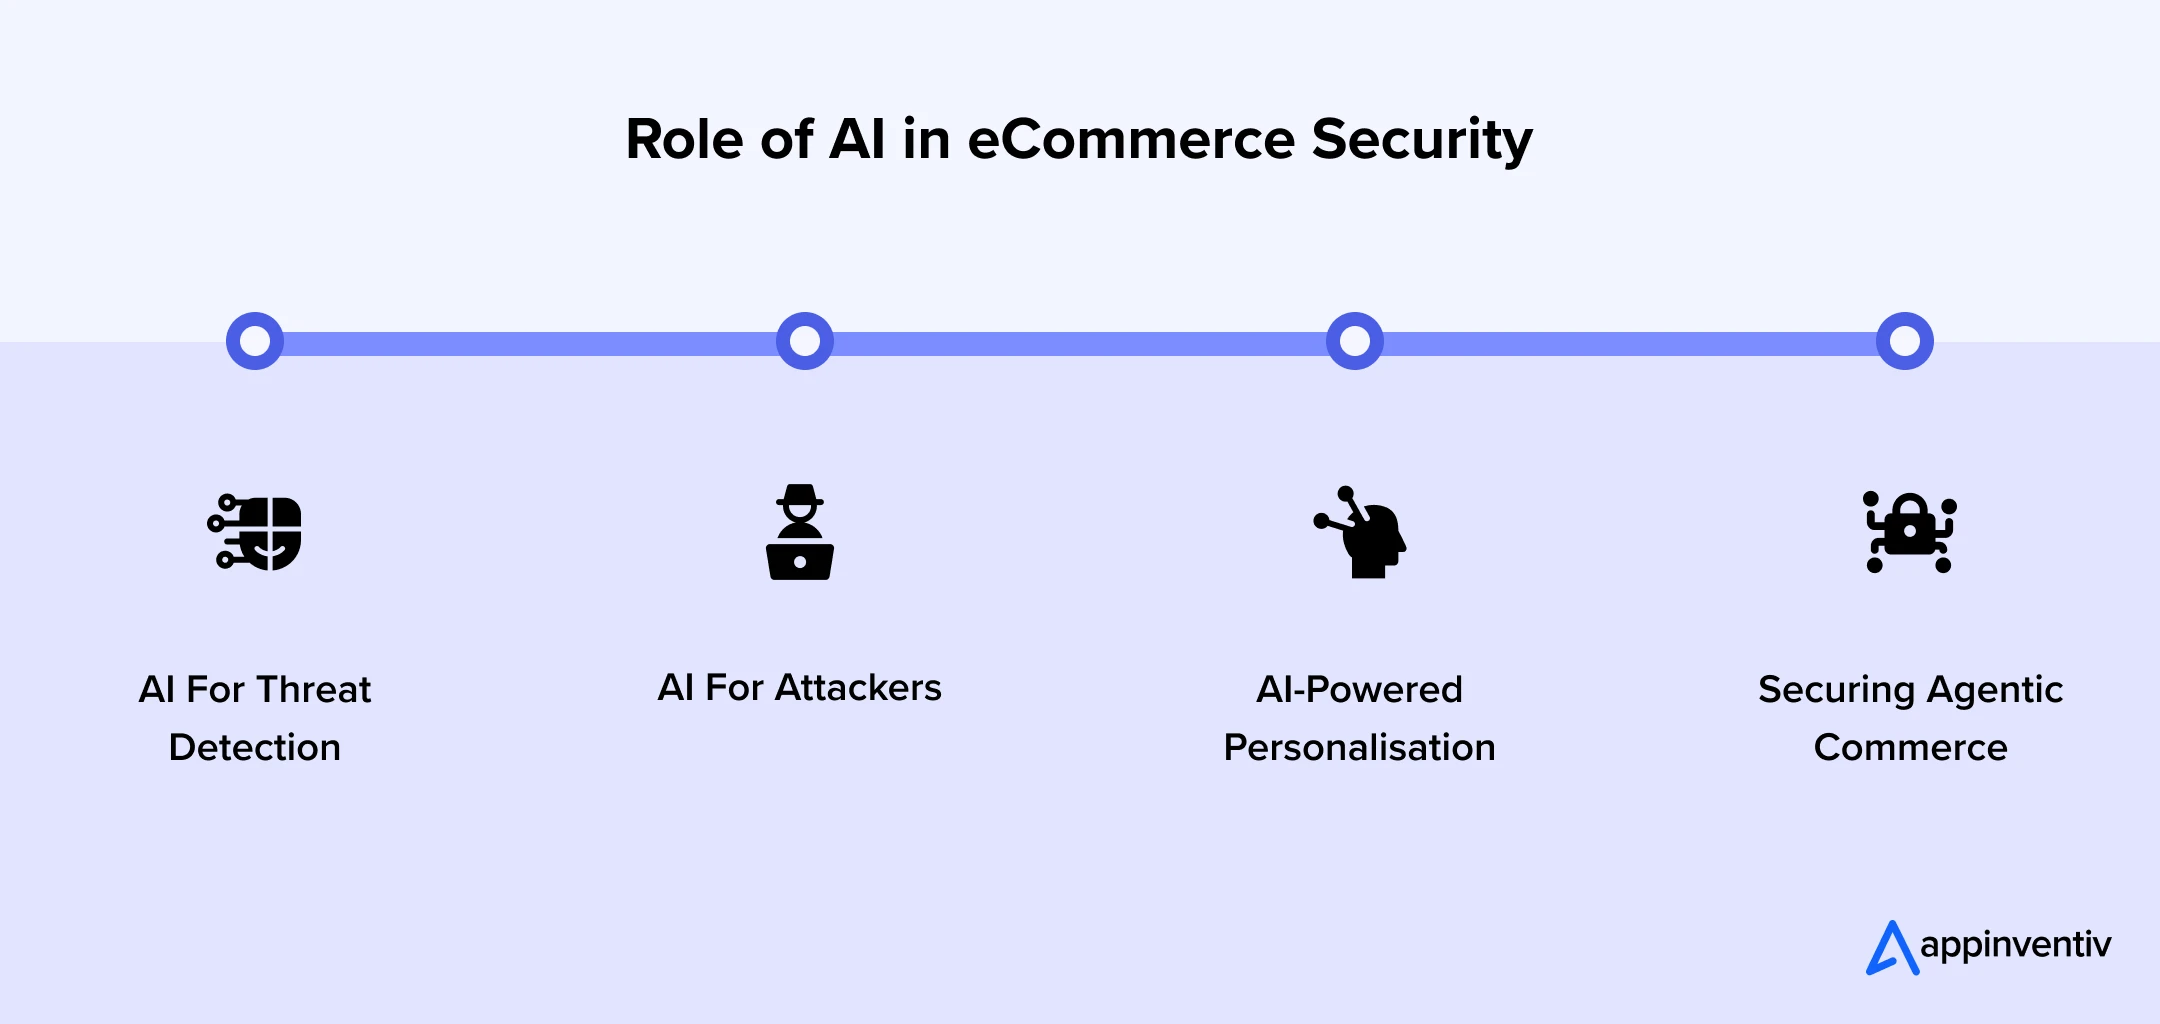
AI For Threat Detection
Machine learning algorithmsanalyze massive traffic datasets to identify subtle behavioral anomalies. This enables the automated blocking of sophisticated fraud attempts in real time
AI For Attackers
Cyber criminals use generative models to craft highly convincing phishing campaigns. AI tools also automate the discovery of zero-day vulnerabilities across distributed platforms
AI-Powered Personalisation
Recommendation engines require access to vast amounts of behavioral data. Security teams must ensure this intelligence is heavily anonymized and protected against extraction
AI Agents in eCommerce
AI agents in retailand eCommerce, capable of browsing, recommending, or transacting, introduce a new authorization problem. Enterprises need clear answers to five questions:
- Who authorises an AI agent to transact?
- How is customer intent verified?
- What happens when an agent follows malicious instructions?
- How are transaction limits enforced?
- How are agent actions audited?
These controls will become increasingly relevant as commerce moves from customer-initiated clicks toward software-mediated purchasing
Ecommerce Security vs Ecommerce Fraud: Where Do They Meet?
Cybersecurity and fraud prevention were historically treated as separate operational silos within the enterprise. Today, the convergence of sophisticated digital attacks means these disciplines heavily overlap. A compromised credential often leads directly to financial loss, requiring unified monitoring strategies
| Ecommerce cybersecurity protects against | Ecommerce fraud controls address |
|---|---|
| Account compromise that gives attackers unauthorized access | Account takeover used to place orders or exploit stored payment methods |
| Credential theft that exposes customer identities | Payment fraud involving stolen or unauthorized payment credentials |
| API abuse that manipulates backend functions | Coupon and promotion abuse that creates unauthorized discounts |
| Malware that compromises devices or commerce systems | Transaction fraud involving suspicious purchases, refunds, or orders |
| Bot attacks that overwhelm or probe commerce systems | Card testing that uses automated transactions to validate stolen cards |
| Data breaches that expose customer or business information | Identity-based fraud using stolen personal information to impersonate customers |
The overlap matters because a compromised account can become a fraud event, while automated fraud activity can reveal an underlying security weakness. Secure commerce programs connect both functions rather than treating them as separate silos
Common Security Mistakes eCommerce Businesses Still Make
Even well-established organizations fall victim to preventable architectural oversight and governance failures. These common missteps leave composable platforms vulnerable to targeted exploitation. Eliminating these operational blind spots is essential for building a resilient enterprise commerce environment
- Treating PCI compliance as a complete strategy rather than just a baseline for security.
- Locking down the website frontend while leaving connected backend APIs exposed and highly vulnerable.
- Granting excessive privileges to internal employees and third-party services without strict access controls.
- Blindly trusting third-party checkout scripts without implementing continuous monitoring or Content Security Policies.
- Holding unnecessary customer data, needlessly expanding the attack surface and increasing compliance liability.
- Relying solely on basic passwords and standard MFA instead of adaptive, risk-based authentication.
- Treating security testing as a pre-launch afterthought rather than a continuous CI/CD process.
- Maintaining data backups but failing to regularly test rapid disaster recovery and restoration processes.
- Siloing fraud prevention and cybersecurity teams instead of combining their overlapping intelligence signals.
- Attempting to bolt security onto a completed architecture rather than integrating it by design.
Incident Response and Recovery: Prepare for When Controls Fail
Even strong controls cannot prevent every incident. Enterprise ecommerce security needs a defined response model that limits disruption, restores critical services, and captures lessons for the next incident
| Stage | Key action |
|---|---|
| Detect | Identify suspicious activity and confirm the affected systems |
| Contain | Isolate compromised accounts, services, or integrations |
| Eradicate | Remove the root cause and close the exploited weakness |
| Recover | Restore trusted systems, validate transactions, and resume operations |
| Learn | Review the incident, update controls, and improve response plans |
How to Assess the Security Maturity of Your Ecommerce Stack?
Security maturity should be measured across the complete commerce ecosystem rather than by counting security tools. The following model will give you good insight for this:
| Level | Security posture | Leadership interpretation | Focus area |
|---|---|---|---|
| Level 1 | Reactive | Security is primarily incident-driven | Basic Identity, Passwords, Manual Recovery |
| Level 2 | Controlled | Core security controls exist and are managed | API Gateways, Standard Payments, Basic Cloud Config |
| Level 3 | Integrated | Security is embedded across development and operations | DevSecOps, Continuous Monitoring, Vendor Risk |
| Level 4 | Adaptive | Real-time risk detection and automated response are established | Advanced Threat Intel, Zero Trust, Incident Response |
| Level 5 | Resilient | Security, fraud, privacy, and resilience operate as one capability | Self-healing Cloud, Unified Fraud Detection, Agentic Audit |
For each level, businesses must comprehensively assess
- Identity: authentication, authorization, MFA, privileged access
- APIs: inventory, authentication, authorization, monitoring
- Payments: PCI controls, tokenization, transaction monitoring
- Data: classification, encryption, retention, access
- Cloud: configuration, identities, segmentation, monitoring
- Third parties: dependency risk, access, contractual controls
- DevSecOps: testing, scanning, secrets, deployment controls
- Monitoring: detection, correlation, alerting
- Incident response: ownership, escalation, containment
- Recovery: backups, restoration, business continuity, testing
4 Key Stages of Ecommerce Security Roadmap: From Vulnerable Stack to Resilient Commerce Platform
Transforming a vulnerable digital footprint into a hardened ecosystem requires a structured, phased roadmap. And a practical roadmap for cyber security implementation is built around 4 integral stages, which are as follows:
Stage 1: Map
Identify all internal microservices, external APIs, and third-party vendor integrations. Establish a comprehensive baseline of exactly where sensitive customer data resides natively
Stage 2: Prioritise
Rank identified vulnerabilities based on their potential impact to business continuity. Allocate engineering re immediately
Stage 3: Harden
Implement zero trust access controls and deploy web application firewalls across the stack. Enforce strict configuration management and immutable infrastructure rules for all cloud deployments
Stage 4: Continuously validate
Integrate automated penetration testing and behavioral monitoring into daily operations. Schedule regular incident response drills to ensure recovery protocols function as intended during crises
Ecommerce Cyber Security Assessment Checklist
Before considering a commerce stack adequately protected, Businesses should be able to answer:
- Is every public API inventoried?
- Are privileged identities protected with strong MFA?
- Can third-party scripts on payment pages be identified and monitored?
- Are payment and refund workflows independently protected?
- Can compromised accounts be detected behaviorally?
- Are cloud identities least-privileged?
- Are secrets centrally managed?
- Are critical dependencies monitored?
- Can the organization isolate a compromised service?
- Have recovery procedures been tested recently?
Use the findings to prioritize the highest-risk gaps first, then build a security roadmap aligned with business impact and recovery needs
What Should eCommerce Cyber Security Implementation Cost?
Ecommerce cybersecurity cost varies significantly because security is tied to every phase, including architecture, transaction volume, regulatory requirements, integrations, data sensitivity, and the number of systems requiring protection
On average, the cost of a secure eCommerce platform developmentranges between $40,000 and $500,000+, depending on your unique project requirements and the risk of vulnerabilities
| Security scope | Estimated investment | Typical focus |
|---|---|---|
| Foundational | $40,000–$80,000 | Security assessment, WAF, IAM, SSL/TLS, baseline hardening |
| Advanced | $80,000–$175,000 | API security, CI/CD controls, monitoring, penetration testing |
| Enterprise | $175,000–$300,000 | Cloud security, CIAM, payment security, integrations, DevSecOps |
| Complex commerce ecosystem | $300,000–$500,000+ | Multi-platform security, modernization, advanced detection, resilience |
The final investment depends on the existing architecture rather than the number of security tools required. Legacy systems, fragmented integrations, custom payment flows, large API estates, multiple cloud environments, and regulatory requirements can materially increase implementation effort, timeline and the cost
The cost of implementing failsafe security in the eCommerce landscape seems substantial at first, but it is just a fraction of the price that a single data breach could cost to a business. In fact, the value a secure eCommerce infrastructure provides in the long run far outweighs the total cost of the project
Preparing for The Future of eCommerce Cybersecurity
The next evolution of digital commerce will be defined by hyper-personalization, headless architectures, and autonomous AI agents. And as the eCommerce landscape and the risks of attack expand, static defenses will become entirely obsolete
Preparing for this next generation of eCommerce platforms needs to combine AI powered threat detection, strong identity controls, API security, payment-page protection, cloud resilience, fraud intelligence, AI governance, and automated security testing
The architectural principle is simple here: assume that any connected component can eventually become compromised, then design the platform so that compromise does not automatically become a business-wide incident
How Appinventiv Helps Build More Secure eCommerce Experiences?
Appinventiv, a trusted provider of cybersecurity consultancy services, approaches ecommerce engineering as a connected product and platform problem, where security, scalability, transaction reliability, and customer experience need to work together
In our 11+ years of delivering eCommerce cybersecurity services, we have successfully delivered over 3000 digital products, including 400+ Secure eCommerce platforms, served 30+ retailers and brands, secured 25+ payment gateway partnerships
And this resulted in a 96% client satisfaction rate, 40% conversion-rate boost through personalization, and 99.50% SLA for transaction reliability
Trusted by Global eCommerce Brands
Our portfolio of eCommerce deliveries include some reputed retail giants like Adidas, IKEA, 6thStreet, Edamama, The Body Shop and so on
- For Adidas, we developed a mobile application, which reached 2 million+ downloads and 500,000+ new users in just a few months of app launch.
- For IKEA, we developed an in-store ERP solution deployed across 7+ IKEA stores, connecting customer onboarding, product catalogs, availability, and promotional activity.
- For6thStreet, we addressed payment-gateway and performance issues, integrated payment options including Checkout.com, Apple Pay, Tabby, and Qpay, and reduced app startup time to under 3 seconds. The project ultimately reached 3+ million iOS downloads and 1+ million Android downloads.
- The Body Shop transformation demonstrates the complexity of enterprise commerce modernization. The platform secured 10 million new users, ₹498 million in digital revenue, 55% faster pages, and 70% fewer manual tasks following the transformation.
- For Edamama, the ecommerce platform supported 20,000+ SKUs and 100,000+ expectant and new mothers, alongside personalized product discovery.
Our team of 1700+ tech architects excels in engineering secure and scalable ecommerce platforms, headless and composable commerce, mobile commerce, API and microservices, cloud architecture, payment integrations, AI-powered personalization, security testing, and legacy commerce modernization
The focus is not simply on adding security controls. We consider architecture, data flows, integrations, CI/CD, identity, and transaction logic together so security does not become a separate layer that conflicts with product delivery
Appinventiv’s Commerce Security Engineering Approach
- Assess: Access architecture, APIs, identities, payment flows, third parties and data.
- Architect: Define trust boundaries, access models, segmentation and resilience requirements.
- Build: Implement secure APIs, CIAM, payment controls, cloud security and DevSecOps.
- Validate: Conduct security testing, threat modeling, configuration validation and attack-path analysis.
- Operate: Monitor, detect, respond and continuously improve.
Our objective is not to declare a platform secure at launch. It is to create an engineering model where security controls evolve with the commerce stack, customer behavior, integrations, infrastructure, and emerging threats
Ready to build security into every layer of your eCommerce operations? Share your pain points with us and get expert guidance to identify security gaps, strengthen your architecture, and build a more resilient commerce platform
Secure Your Commerce Stack Today
FAQs
Q. What are common data breach prevention services for online businesses?
A. Enterprise data breach prevention services typically include Web Application Firewalls (WAF), advanced Bot Management, and automated API Security gateways. Additionally, organizations rely on Customer Identity and Access Management (CIAM) platforms, network tokenization for payment processing, and continuous threat intelligence monitoring to identify vulnerabilities before exploitation occurs
Q. What are some key types of eCommerce security measures?
A. The primary types of eCommerce cyber security measures include application security for the storefront, API security for headless architectures, and data security to protect customer intelligence. It also encompasses network security to block unauthorized traffic, endpoint security for physical retail devices, and robust access management to control internal permissions. Building an ecommerce cybersecurity framework requires integrating all these disciplines seamlessly.
Q. What is the role of cybersecurity in eCommerce companies?
A. The fundamental role of cyber security in eCommerce companies centers on protecting sensitive customer intelligence, securing financial transactions, and ensuring continuous platform availability
Director & Co-Founder
Prev Post
Captcha:3 + 4 =
Looking for a marketing partner? Let our experts at Appinventiv Digital reach out to you.
Fast 2-minute response, fully NDA-protected

Related:
<a href="https://yoursite.com/automation-training-benin/” title=”Digital Automation Training Benin: 5 Winning Skills Employers Demand in 2026″>
Digital Automation Training Benin: 5 Winning Skills Employers Demand in 2026
WhatsApp Marketing Automation Africa: 6 Dangerous Mistakes Brands Make in Nigeria
Want to learn this practically?
Join Justfine Infotech and build real digital skills in AI, automation, web development, digital marketing, office productivity, e-commerce, freelancing and cybersecurity.
Available Programmes:
6 Weeks Certificate • 3 Months Professional Certificate • 6 Months Diploma • Full Professional Diploma
WhatsApp:
+229 01 57 57 99 15
+229 01 66 68 11 60
Source: appinventiv.com
 English (UK)
 Français